Generate all design docs, from the context graph that grows with the engagement
— AI-powered.
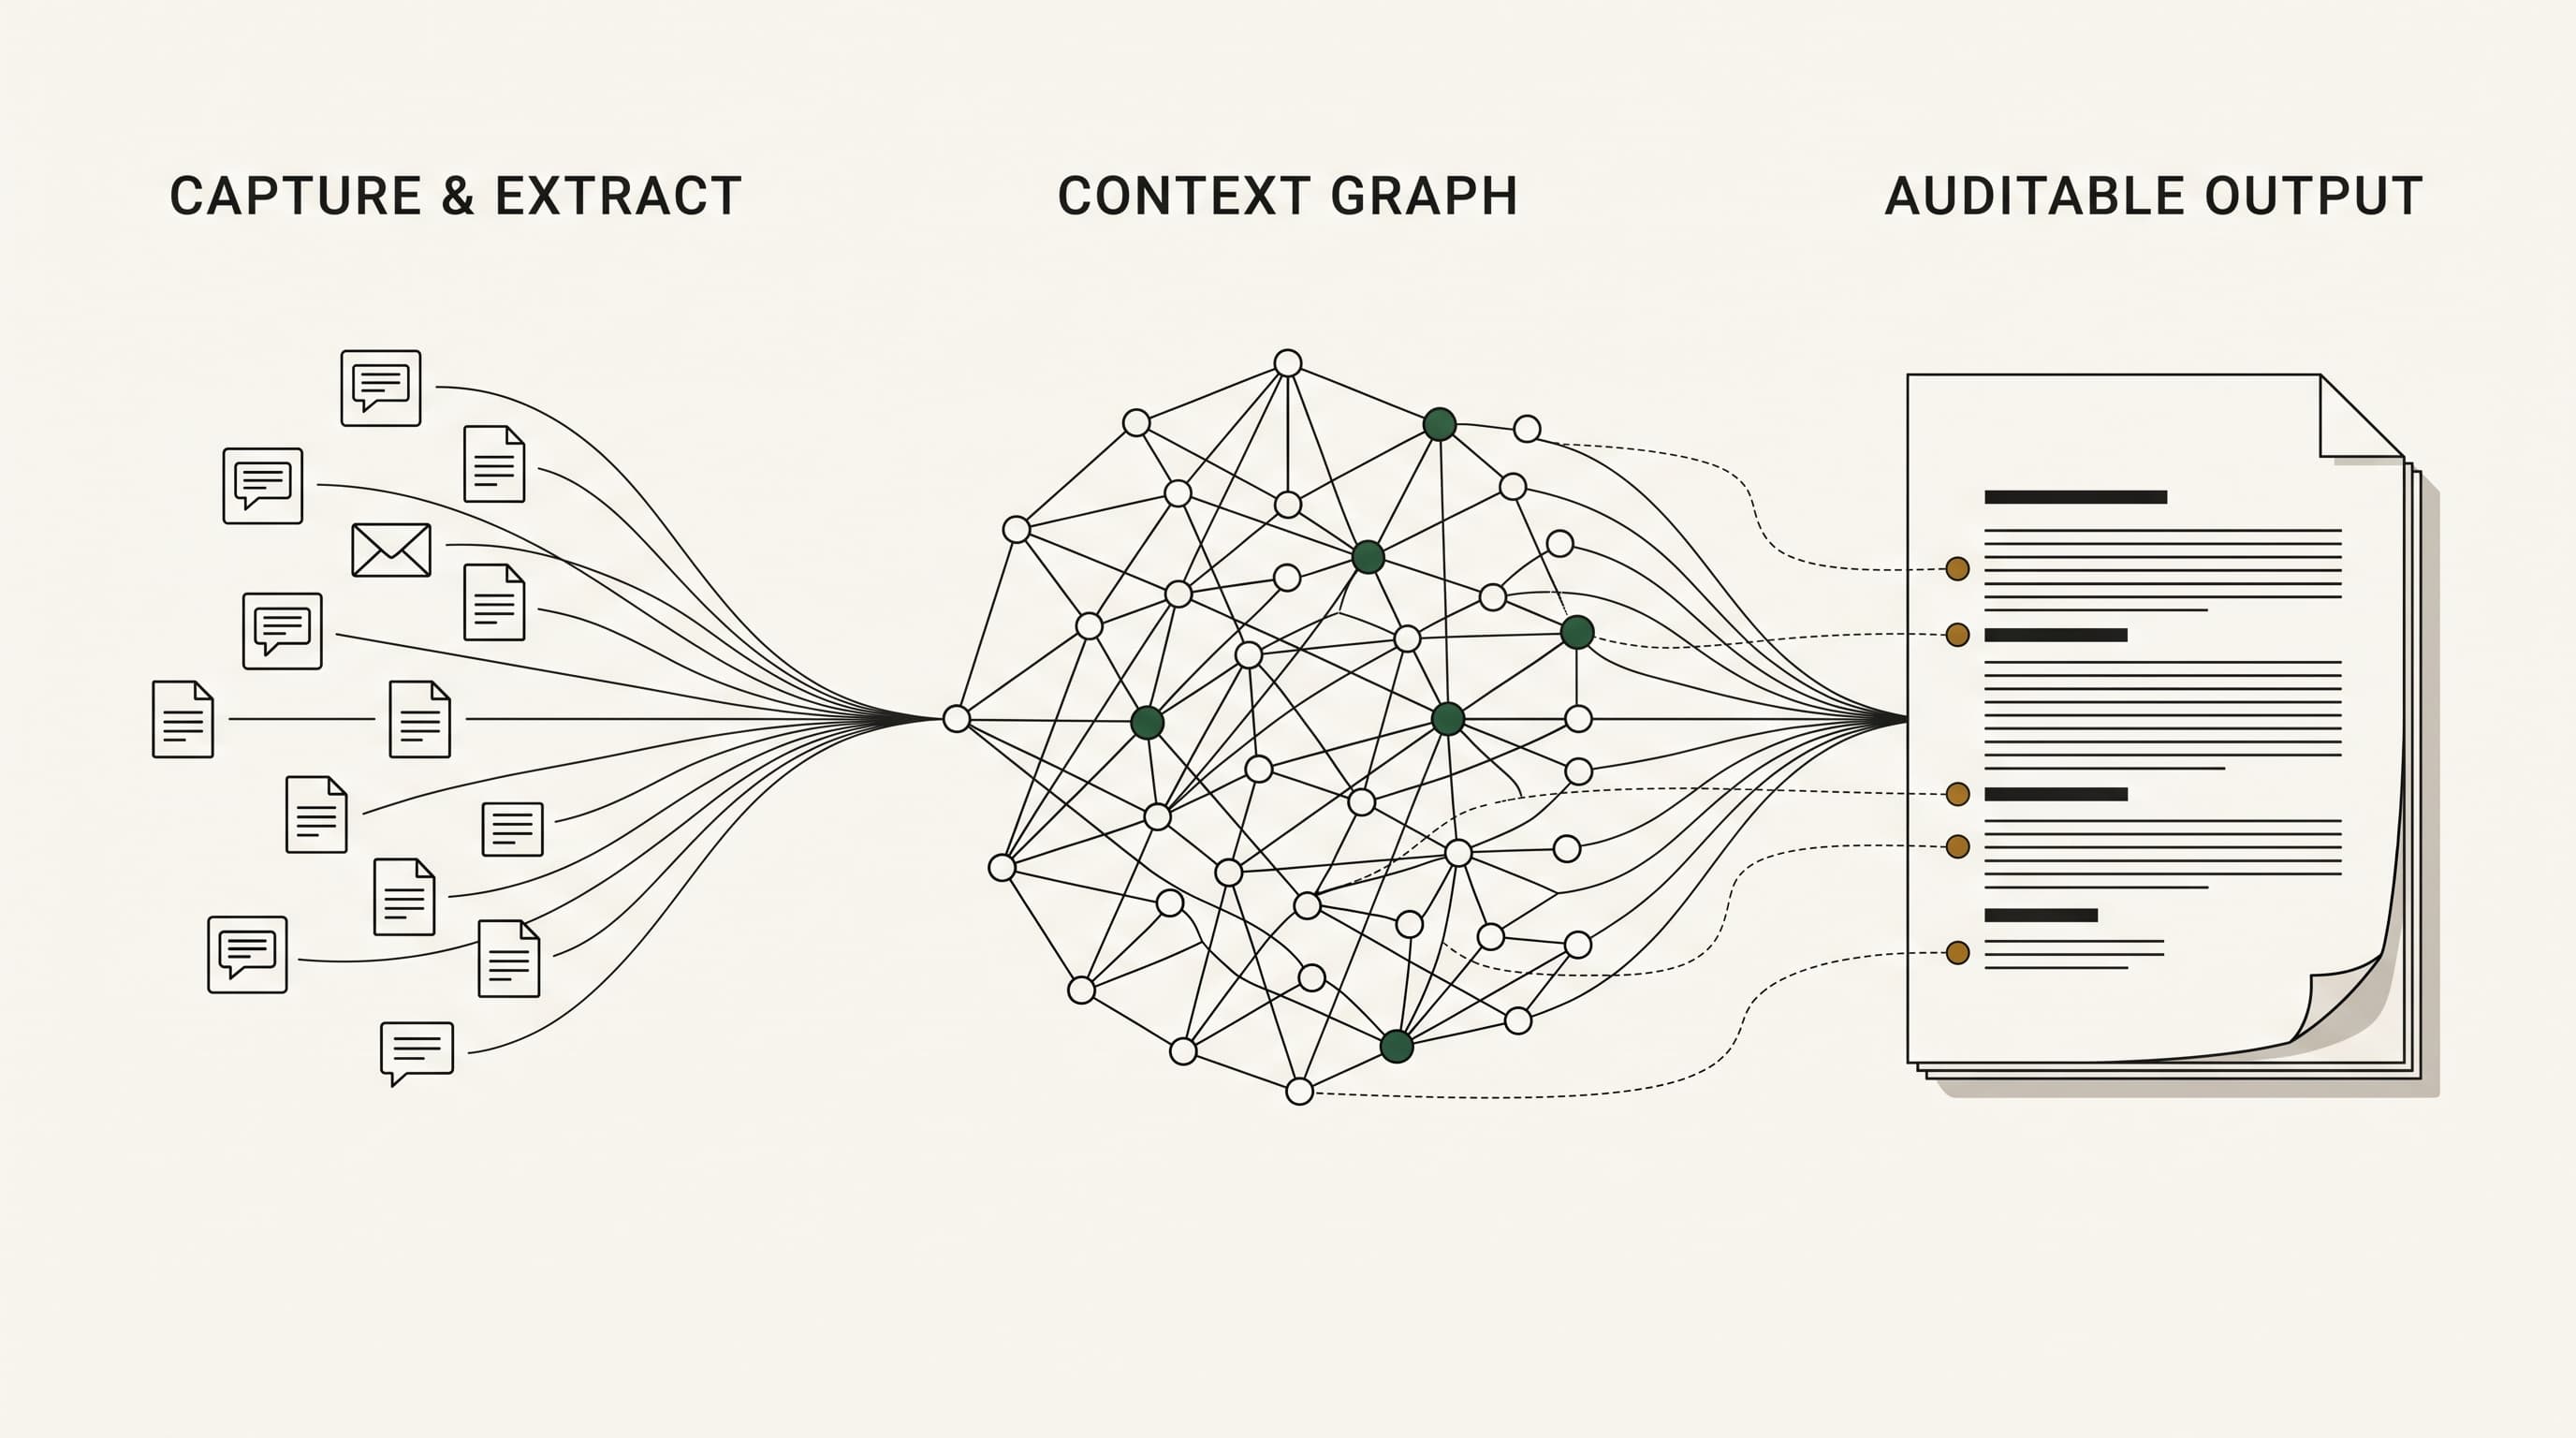
Artefae ingests and extracts context from all chat, email and files into a context graph, then generates the auditable artefacts — System Design Documents (SDD), Architecture Decision Records (ADR), Requirements & Scope Documents (RSD), etc.
Why Artefae
Every second spent writing documentation is a second not spent building. Artefae writes from what you already have.
Never write from scratch
Documentation drafts from your actual conversations and decisions, not templates. Every claim is sourced.
Gaps are visible
See missing decisions before the draft goes to the client. Not after handoff, not in production.
Context preserved
All rationale stays intact. Why decisions were made, not just what was decided.
Fully traceable
Every sentence links back to the Slack message, email, or note that justified it.
Works with your tools
Capture from Slack, email, git, ADRs, diagrams. Process once, generate many.
Compliance ready
Audit trail included. Who contributed what, when, and where it ended up.
Built for industry standards
Artefae generates artifacts aligned with industry frameworks and best practices. Choose your role, get compliant documentation.
Forward Deployed Engineer
fde
Technical implementation, system design, integration & deployment
SDD, ADR, HLD, LLD/TDD, RSD, Specs, Runbook, Risk Assessment, Performance, Threat Model
Solutions Architect
solutions_arch
Solution design, RFP responses, business case analysis & implementation planning
SAD, HLD, LLD/TDD, ADD, RFP, Brief, Business Case, RTM, Roadmap, Tech Eval, Gap Analysis, Risk Mitigation, KPIs
Enterprise Architect
enterprise_arch
Enterprise strategy, governance, compliance & long-term alignment
EA Strategy, Reference Arch, Current/Target State, Capability Assessment, Roadmap, Governance, Compliance, Portfolio Impact, Tech Debt, Skills Gap, Change Mgmt, Integration Framework, Data Architecture
Cyber Security Responder
cyber_responder
Incident response, forensics, threat analysis & compliance
Incident Report, Timeline, Forensics, RCA, Threat Assessment, Security Impact, Remediation, Risk/Exposure, Lessons Learned, Evidence, Regulatory Notification, Communication Log, Vulnerability Assessment, Detection Capability
Fractional CTO
cto
Tech strategy, organizational health, risk & business alignment
Tech Strategy, Risk Register, Org Structure, Skills Gap, Tech Debt, Vendor Eval, Hiring Plan, Budget, Roadmap, Eng Culture, Governance, Metrics/KPIs, Security Posture, Innovation Strategy, Outsourcing Analysis
Penetration Tester
pt
Vulnerability assessment, risk quantification & compliance
Pentest Report, Detailed Findings, Vulnerability Assessment, Risk Quantification, PoC Documentation, Remediation Roadmap, Exec Risk Summary, Security Recommendations, Compliance Mapping, Infrastructure Assessment, App Assessment, Social Engineering Report, Re-test Report, Metrics/Trends, Red Team Report
81 document types across 6 specialized personas, each aligned with industry best practices and frameworks.
Generate, export to Markdown / PDF / DOCX / HTML, and maintain full audit trail and compliance.
Shaped for your work
Choose your engagement type. Get the personas and artifacts that matter.
🏗️ Implementation & Design
Architecture Review · Forward Deployed Engineering
You're building systems, evaluating designs, making architectural decisions. Working hands-on or assessing choices.
Available Personas
Artifacts Generated
🔐 Security & Compliance
Penetration Test · Security Response · Compliance Audit
You're assessing security posture, responding to incidents, or preparing for regulatory audits.
Available Personas
Artifacts Generated
💡 How It Works
Pick Your Engagement Type
Choose the type of work you're doing. This immediately filters which personas are available for that engagement.
Architecture Review selected
→ Show: FDE, Solutions Architect, Enterprise Architect, CTO
✗ Hide: Penetration Tester, Cyber Responder
Select Your Persona
Each persona generates only artifacts that make sense for your engagement type. Never cross-type pollution.
Enterprise Architect selected
→ Generate: SDD, ADR, Tech Risk Assessment
✗ Hide: Integration Specs, Deployment Runbooks
How it works
Four steps. CLI or web app. From capture to audit trail.
Capture
Point it at notes, Slack, transcripts, or git. Extraction happens automatically—decisions, constraints, systems extracted with full context and confidence scores.
artefae capture ./notes.mdUpload files or paste content in the web app
Review
Inspect the extracted knowledge graph. Fill gaps, resolve ambiguities, approve decisions before they become artifacts.
artefae reviewReview in dashboard → Entities tab
Generate
SDDs, ADRs, RSD grounded only in what you have. Gaps flagged, never guessed.
artefae generate sddGenerate → Select artifact type & persona
Export
Markdown, Word, or straight to git with full audit trail and provenance links.
artefae export --to gitExport → PDF, DOCX, Markdown, or HTML
CLI (Power Users)
Full automation. Integrate Artefae into your CI/CD, scripts, or local workflows.
- ✓Batch processing & automation
- ✓Git integration for version control
- ✓Scriptable end-to-end workflows
- ✓No browser required
Web App (Collaborative)
Point-and-click interface. Share engagement links, collaborate in real-time, manage multi-workspace teams.
- ✓Real-time collaboration
- ✓Multi-workspace & team management
- ✓Role-based access control
- ✓Compliance dashboard & audit logs
From conversation to decision
See how a single Slack thread becomes structured knowledge and auditable decisions.
We need to decide on the database strategy. PostgreSQL vs MongoDB?
PostgreSQL for ACID compliance. Finance team has strict audit requirements.
Agreed. We also need redundancy across 2 regions for 99.9% uptime.
Extracted Knowledge
- ✓Use PostgreSQL for ACID compliance
- ✓Multi-region redundancy (2 regions)
- ⚡Finance audit requirements
- ⚡99.9% uptime SLA
- 👤Alice (Tech Lead)
- 👤Bob (Backend)
- 👤Carol (Infrastructure)
“A template tells you what to write. Artefae tells you what’s actually true — and proves it with sources.”
Artefae vs Claude Cowork
Extraction vs. Synthesis
Artefae is purpose-built for professional client deliverables. Claude Cowork is great for ad-hoc exploration. Here's how they differ.
"Artefae is to security/architecture deliverables what GitHub Copilot is to code." It's purpose-built for professional engagement artifacts: automatically captures context, extracts what matters, and generates standards-compliant documents that are reproducible, auditable, and ready for client delivery.
| Dimension | Claude Cowork | Artefae |
|---|---|---|
| Reproducibility | No Different output each time | Yes Identical (deterministic) |
| Hallucination Risk | High Invents details | Zero Extraction-based only |
| Audit Trail | None Not compliant | Full Compliance-ready |
| Setup Time | ~40 minutes manual file organization | 2 minutes automated capture |
| Source Traceability | None — where did this come from? | 100% Every statement sourced |
| Batch Generation | One artifact at a time | 10+ parallel artifacts |
| Standards Compliance | Manual verification required | Automated IEEE 1016, NIST, PTES, etc. |
| Cost per Artifact | $0.19 (synthesis-based) | $0.01 extraction + minimal synthesis |
| Best For | Ad-hoc exploration, internal use | Client deliverables, compliance, scale |
10 Engagements/Month (30 Artifacts)
10 Engagements/Month (30 Artifacts)
When to Use Claude Cowork
- ✓Ad-hoc exploration
- ✓Internal use only
- ✓One-off projects
- ✓Speed over accuracy
When to Use Artefae
- ✓Client delivery artifacts
- ✓Compliance requirements
- ✓Security/architecture engagements
- ✓Cost-sensitive at scale
- ✓Professional delivery (standards-compliant)
- ✓Batch generation (10+ artifacts)
For internal brainstorming and exploration, Claude Cowork is simpler. For professional client deliverables, compliance, and reproducible outputs, Artefae is 10-100x more capable.
→ See For YourselfFrequently Asked Questions
Everything you need to know about Artefae. Can't find your answer? Contact our support team.
Still have questions?
Contact our support teamStart on your next engagement, not your last.
Context captured from day one is worth more than context reconstructed on day forty.
→ Get started free